Machine builders
Get your machine accepted by the customer's IT and OT
You deliver machines with control systems to industry. Your customers' IT and OT teams set ever higher security requirements. The EU adds new ones through the Cyber Resilience Act and the Machinery Regulation. XoT helps you meet several of them without redesigning the machine.
The situation
What machine builders face today
The customer wants to control access
The customer's IT and OT teams want to know who reaches the machine, when and why. They often require personal accounts and multi-factor authentication.
The customer wants logs
Every remote connection must be traceable afterwards. Ideally the logs go to the customer's own SIEM.
No openings into the network
Firewall rules for outbound traffic are often accepted. Rules for inbound traffic are almost never accepted.
New EU requirements
The Cyber Resilience Act sets requirements for products with digital elements. The Machinery Regulation requires protection against manipulation of the control system.
How XoT helps
The customer's requirements and what XoT does
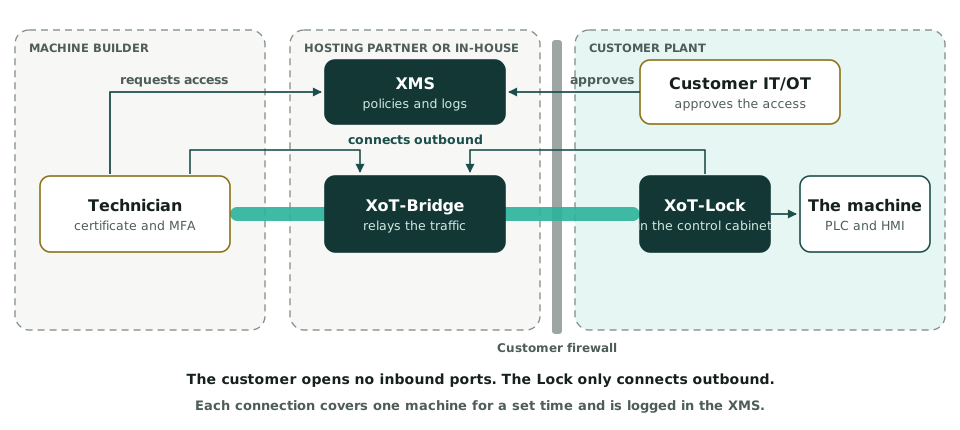
| Customer requirement | What XoT does |
|---|---|
| No inbound ports | The Lock in the machine only connects outbound to the XoT-Bridge. The customer only needs to allow outbound traffic. |
| Personal accounts | Every technician has their own certificate. Sign-in goes through an identity provider, such as Entra ID, with multi-factor authentication. |
| The customer decides | The technician requests access in the XMS. Someone at the customer can approve the request. Access covers one machine for a set time. |
| Logs | The XMS logs every connection and every policy change. The logs can be sent to the customer's SIEM. |
| Recorded sessions | Sessions through XoT-WebAccess are recorded automatically. |
| The machine is invisible | The control system behind the Lock is invisible on the customer's network to anyone without permission. |
| Machine to machine | The Lock can hold an encrypted connection to another Lock, for example at a monitoring server. |
Installation
The Lock in the machine or next to it
In the control cabinet
XoT-S1 mounts on a DIN rail in the machine's control cabinet. An adapter is available for 24 V cabinets.
In the router
Does the machine have a Teltonika router for the mobile network? Then the Lock can be installed as a package in the router.
As software
The Lock can run on an industrial PC or a virtual machine, on x86 or ARM64.
Built into new machines
The Lock becomes part of the machine. It is then included in your risk assessment and in the technical documentation for the CRA and the Machinery Regulation.
Added to machines already in the field
The Lock is installed in front of a machine that is already at the customer site. The machine does not need to change. Check whether the addition counts as a substantial modification of the machine.
Cyber Resilience Act
CRA security requirements where XoT helps
A machine with a control system and a network connection is often covered by the Cyber Resilience Act. The reporting obligation has applied since 11 September 2026. Most other requirements apply to machines placed on the market from 11 December 2027.
Annex I of the regulation lists security requirements for the product. The table shows the requirements where XoT can be part of the solution. Rows where XoT helps are highlighted in green.
| Annex I, Part I | Area | XoT |
|---|---|---|
| 2(d) | Protection from unauthorised access, with authentication and access management | Yes |
| 2(e) | Confidentiality, for example through encryption | Yes |
| 2(j) | A limited attack surface, including external interfaces | Yes |
| 2(f) | Protection of data and commands against manipulation | Partly |
| 2(k) | Reduced impact of an incident | Partly |
| 2(l) | Logging of access and changes | Partly |
| 2(a) | No known vulnerabilities when the product is delivered | No |
| 2(c) | Security updates for the product | No |
Yes applies to network access to the machine. Partly means that XoT protects and logs the traffic through the Lock, but not what happens inside the control system. The descriptions of the requirements are our simplifications.
XoT does not make the machine CRA-compliant. As the manufacturer, you show that the machine meets the requirements. XoT can be part of how you do it.
Read about the Cyber Resilience ActRead about the Machinery Regulation
Your responsibility
What you remain responsible for
- the risk assessment of the machine, for both safety and cybersecurity
- vulnerabilities in the control system and in your own software, and updates for them
- the software bill of materials (SBOM) for your machine
- the technical documentation and the EU declaration of conformity
- reporting actively exploited vulnerabilities in your machine to ENISA
Xertified as a supplier
Material for your assessment of us
The CRA requires you to exercise due diligence when you integrate components from other manufacturers. That is Article 13(5). So we show openly how we meet the requirements ourselves.
Five years of support
All our products are supported for five years. Security updates are free of charge.
Class I
Our assessment is that XoT-Lock and XMS are Class I important products.
Reporting to ENISA
We have reported actively exploited vulnerabilities in our products since 11 September 2026.
Documents on request
SBOM and penetration-test reports. The product description for your technical file can be downloaded directly.
Download the product descriptionRequirements that apply to XertifiedQuality and security
Hosting and partnership
Who runs the system?
The XMS is the server that holds the policies and the logs. Often a hosting partner runs the XMS for the machine builder. If you have your own IT operations, you can run the XMS yourselves.
Machine builders who offer XoT to their customers become Xertified partners.
Common questions
Does XoT make the machine CRA-compliant?
Not on its own. XoT helps with some of the security requirements, such as protection from unauthorised access, encryption and logging. You assess the machine as a whole.
Does the customer have to open anything in the firewall?
Not for inbound traffic. The Lock connects outbound to the XoT-Bridge. The customer only needs to allow that outbound traffic.
Who approves when a technician wants to connect?
You decide that together with the customer. Often someone at the customer approves. A technician cannot approve their own request.
Does it work over the mobile network?
Yes. XoT works over any IP network, including mobile networks. The Lock can also be installed in Teltonika routers.
Can we get material for the technical file?
Yes. The product description shows how XoT works, how it is protected and what it means for the Machinery Regulation and the CRA.
This is our reading of the regulations, not legal advice.
Want to offer XoT with your machines?
We are happy to explain how you become a partner and how XoT can be fitted to your machines.