Quality
How we work with quality and security
This page helps you assess us as a supplier, for example in a procurement. It describes how we develop, test and update XoT.
Requirements that apply to XertifiedHow XoT helps with your requirements
Quick answers
Answers to common procurement questions
| Question | Answer |
|---|---|
| How long is each product supported? | For five years. That applies to XoT-S1, XoT-Lock, XMS and the clients. |
| How are security updates delivered? | A long-term release comes every year. It gets security updates for five years. The updates are free of charge. |
| Is Xertified ISO/IEC 27001 certified? | Not yet. We plan to certify. |
| Is XoT certified to IEC 62443? | No. Our development follows the practices in part 4-1. We claim no level. |
| Is Xertified covered by NIS2? | No, the company is below the size threshold. We meet the requirements customers place on their suppliers. |
| Does the Cyber Resilience Act apply? | Yes. We have reported under the regulation since 11 September 2026. XoT-Lock and XMS are Class I. |
| Is XoT-S1 CE-marked? | Yes. It passed EMC testing at an accredited laboratory. |
| Where is customer data hosted? | XMS is hosted in Sweden by default. It can also run in the US or on your own premises. |
| Do you share an SBOM and penetration-test reports? | Yes, on request. Test reports are shared under an NDA. |
| How do we report a vulnerability? | Email security@xertified.com. We confirm receipt within five working days. |
| Who is the security contact? | Our CTO. That includes reporting under the Cyber Resilience Act. |
An SBOM, or software bill of materials, lists the components the software is built from.
Quality management
A quality management system
We run a quality management system. It covers design, development, production, testing, deployment and maintenance. It applies to both the hardware and the software in XoT.
The system prevents defects through defined methods. It also finds and fixes the defects that still occur.
CEO
Owns the quality management system. Accountable for quality, information security and data protection.
CTO
Responsible for product security, testing and vulnerability handling. Single point of contact for reporting under the Cyber Resilience Act.
Risks are assessed every year
We assess risk at least once a year and whenever something material changes. That covers risks to deliveries and support, vulnerabilities in our products and risks at our suppliers. We review the threat landscape at least twice a year.
Our quality objectives
- No known critical vulnerability is left unaddressed in a supported release.
- Customers and partners should be satisfied. We follow this up through support cases and feedback.
- XoT keeps protecting your equipment when the XMS cannot be reached.
- We meet the regulations that apply to us on time. We say plainly which ones do not apply.
- Quality and security work is planned and budgeted.
Management reviews the work every year
The review draws on customer feedback, support cases, audits and test results. Among other things, we track how many defects are found and how quickly they are fixed.
Secure by design
Security is built in during development
XoT is developed with a secure development life cycle. It is based on Microsoft SDL, Microsoft's method for secure development. We test in every development cycle. Part 4-1 of IEC 62443 is our reference for how development is done.
Denied by default
The Lock lets through only traffic that a rule allows. Equipment behind the Lock is invisible to anyone without permission.
No passwords
Every person and every device has its own certificate. The key can be held in the computer's TPM security chip, on a smart card or in a hardware key.
Encrypted traffic
Traffic is encrypted with WireGuard. The user and the Lock check each other twice a minute.
Protection continues
The Locks keep enforcing the rules even when the XMS cannot be reached.
Changes are logged
Every change to rules and permissions is written to a log. The log is protected against later modification.
Read about the architectureSecurity when AI finds the vulnerabilities
Updates and support
Security updates are free of charge
The support period is five years for all our products. During that time you get security updates free of charge.
| Item | What we do |
|---|---|
| Support period | Five years for XoT-S1, XoT-Lock, XMS and the clients. |
| Long-term releases | One a year. Each long-term release gets security updates for five years. |
| Feature releases | About once a quarter. They are not patched after the next release. |
| Moving to a long-term release | Free for every customer, from any release, with or without a licence. |
| Security updates | Free of charge, for the latest release and for long-term releases within their five years. |
| New features | Require a valid licence. |
| Support | Working days 08–17 Swedish time. Your partner provides first-line support. We provide second and third line. |
The product keeps working if the licence lapses. You can always stay on a release that gets fixes.
Testing
How we test XoT
Software
We test functions and performance and check that old defects do not return. We also run static code analysis and fuzzing, which means testing with random input.
Hardware
We validate the design and test how the hardware handles interference, stress and different environments. We also test whether the hardware can be attacked.
The whole
The software is validated on the hardware before release. Testing is done in environments that resemble customer networks.
External testing
Our partners penetration-test XoT. Some customers test it more often themselves. The reports are available on request under an NDA.
Customers, partners and researchers are welcome to review XoT. We first agree on the rules and sign an NDA.
Hardware
XoT-S1 is made in Sweden
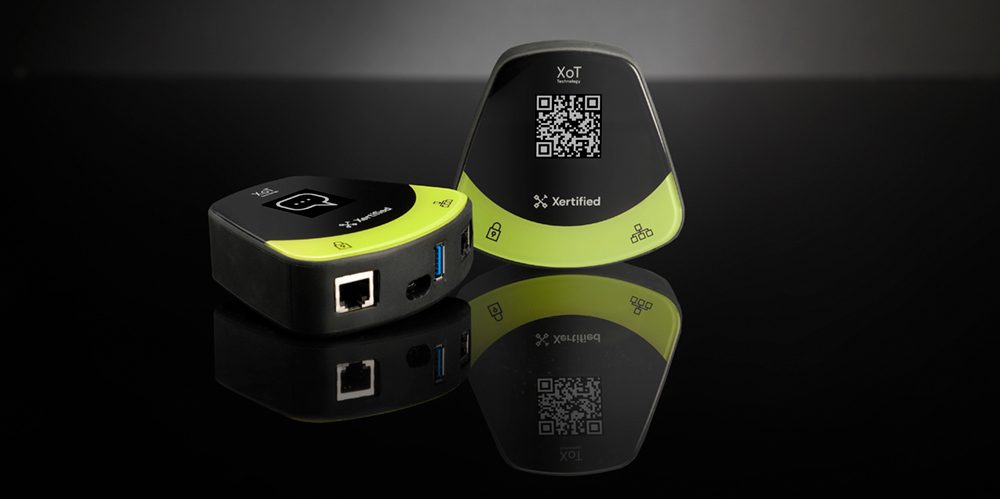
XoT-S1 is designed and manufactured in Sweden. It operates from −28 to 75 °C and has no moving parts. It mounts on a DIN rail. It runs on 5 V DC over USB-C and has no radio.
The Lock is also available as software, as a virtual machine and for Teltonika routers.
Suppliers and incidents
Suppliers, incidents and our own security
Suppliers
We assess hardware suppliers for quality and security. They must follow secure manufacturing practices, and we require regular audits.
Components
We monitor vulnerabilities in the software and hardware that XoT is built on. We also track known defects and vulnerabilities in XoT.
Incidents
We have an incident response plan and playbooks. Every September we review the plan, run an exercise and train our staff.
Our own security
We use multi-factor authentication and hardware tokens wherever our services support them. Secrets are kept in key vaults.
Training
All employees and contractors are trained at least once a year. The training covers quality, secure development and cybersecurity.
Hosting and data
Where data is kept and how long logs are stored
- XMS is hosted in Sweden by default. It can also run in the US or on your own premises.
- XMS processes user identities and access logs. When we host the XMS for you, we act as processor.
- XMS keeps logs for up to 36 months. Do you need to keep them longer? Then send them to your SIEM.
- Test and pilot environments hosted by us come without an availability commitment.
Documents
Documents you can get
| Document | How to get it |
|---|---|
| Quality at Xertified, this information as a document | On request |
| Software bill of materials (SBOM) | On request |
| Penetration-test reports | On request, under NDA |
| Report of known issues | On request |
| Description of logging and telemetry in XMS | On request |
| Technical data, EMC test report and EU declaration of conformity for XoT-S1 | On request |
| XoT Technology and Your Compliance, on how XoT helps with your requirements | On request |
| Product description for the machine builder's technical file | Download (PDF) |
| Support terms and response times | On request |
| Installation and hardening guides | docs.xertified.com |
Do you have questions about compliance or procurement? Email sales@xertified.com. Send questions about vulnerabilities and security to security@xertified.com.
Assessing us as a supplier?
We are happy to send the documents. We also answer questions in procurement specifications.